PHP2Shell: Critical PHP Flaws Force Sites Offline, Patch Now
Two critical PHP flaws dubbed PHP2Shell, both rated CVSS 9.2, led to sites going offline worldwide. Germany's BSI issued an orange alert and urges immediate updates.
Two critical vulnerabilities in the PHP runtime, grouped under the name PHP2Shell, prompted numerous websites worldwide to go offline as a precaution on Wednesday. Germany's Federal Office for Information Security (BSI) issued a level 3 "Orange" cybersecurity warning, the second-highest tier, and advised operators to disconnect affected web servers from the internet if in doubt.
The flaws, tracked as CVE-2026-109618 and CVE-2026-109619, each score 9.2 on the CVSS scale. Government agencies in Finland and the Netherlands, parts of the BBC, German municipalities, hospitals and universities temporarily took services offline.
Why the bug reaches so far
According to security firm Wiz, PHP powers roughly 70 percent of websites, though that figure cannot be independently verified. Because the bug sits in the runtime itself, systems such as WordPress, Drupal, Joomla, Typo3, Magento, Nextcloud and MediaWiki are exposed even if their own code is sound.
Wiz describes four related memory-safety flaws reaching back to PHP 5.4. After a crafted request triggers a memory overflow, PHP aborts and frees memory but does not fully clear internal references. The next request handled by the same worker can then access memory containing attacker-supplied code, a pattern known as use-after-free. Without logging in, attackers can run code remotely or read passwords, API keys and session data, similar to Heartbleed.
The PHP Foundation says signs of one flaw surfaced in 2024 during an audit by Quarkslab for the Sovereign Tech Agency, but it stayed unfixed for lack of agreement and a known attack path. Calif and OpenAI showed on 11 August 2026 that a practical attack was possible, using GPT-5.6 Sol. Wiz found the same family independently eight days later and also used a pre-release version of Google Deepmind's Gemini 4 Argon. Chaining such bugs once took months; language models now do it in hours.
What administrators should do
PHP released fixed versions 8.5.12, 8.4.27, 8.3.36 and 8.2.35, plus backports for the expired 7.4, 8.0 and 8.1 branches. Apache with mod_php carries the highest risk. Web application firewalls such as Cloudflare's do not offer complete protection, and Docker images must be rebuilt.
As a stopgap, the developers suggest setting session.upload_progress.enabled=0 and memory_limit=-1. Admins should check logs for clusters of HTTP 500 errors and unusually large PHPSESSID cookies. The Dutch NCSC-NL maintains a list of affected third-party products, including pfSense and OPNsense.
Apps worth a look
 SUMO: the number puzzle
Tap the right tiles, add them up, hit the target. Easy to learn, hard to master. Free, for all ages.
 Dialo: learn languages by speaking
Talk to an AI conversation partner; every sentence comes back corrected and explained in your language. 9 languages, A1 to C2.
 ediviewer: read EDI files like documents
Open EDIFACT and X12 messages, see every segment explained, convert to JSON/XML, export PDF and Excel. Runs locally, no upload.
More from this day
See all →
ESA-backed JASPER system will warn pilots of GPS spoofing
Iron Warriors: Polish Students' Car Covers 837 km on One Litre
ESA's Space HPC supercomputer packs 5 petaflops for space data
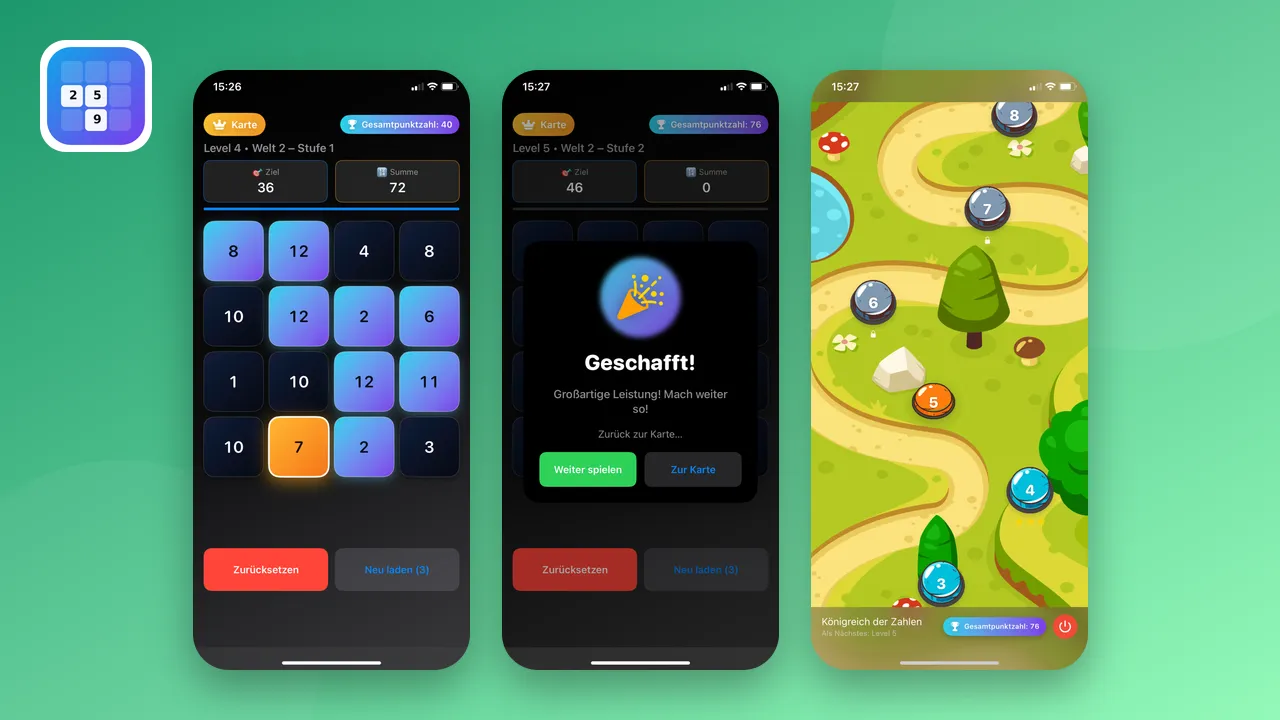
SUMO Number Puzzle Turns Mental Math Into a Free Mobile Game
More in: Security
See all →
Cohere Says Alibaba's Qwen3.8-Flash-Next Tried to Send a File to Beijing
SMS of Death: Android Flaw Lets One Text Crash Phone Service

CrowdStrike: Four Hacker Groups Ran Attacks With Claude Code
