NTT Docomo Breach Exposed Plan Details and Bank Data of Up to 294,839 Lines
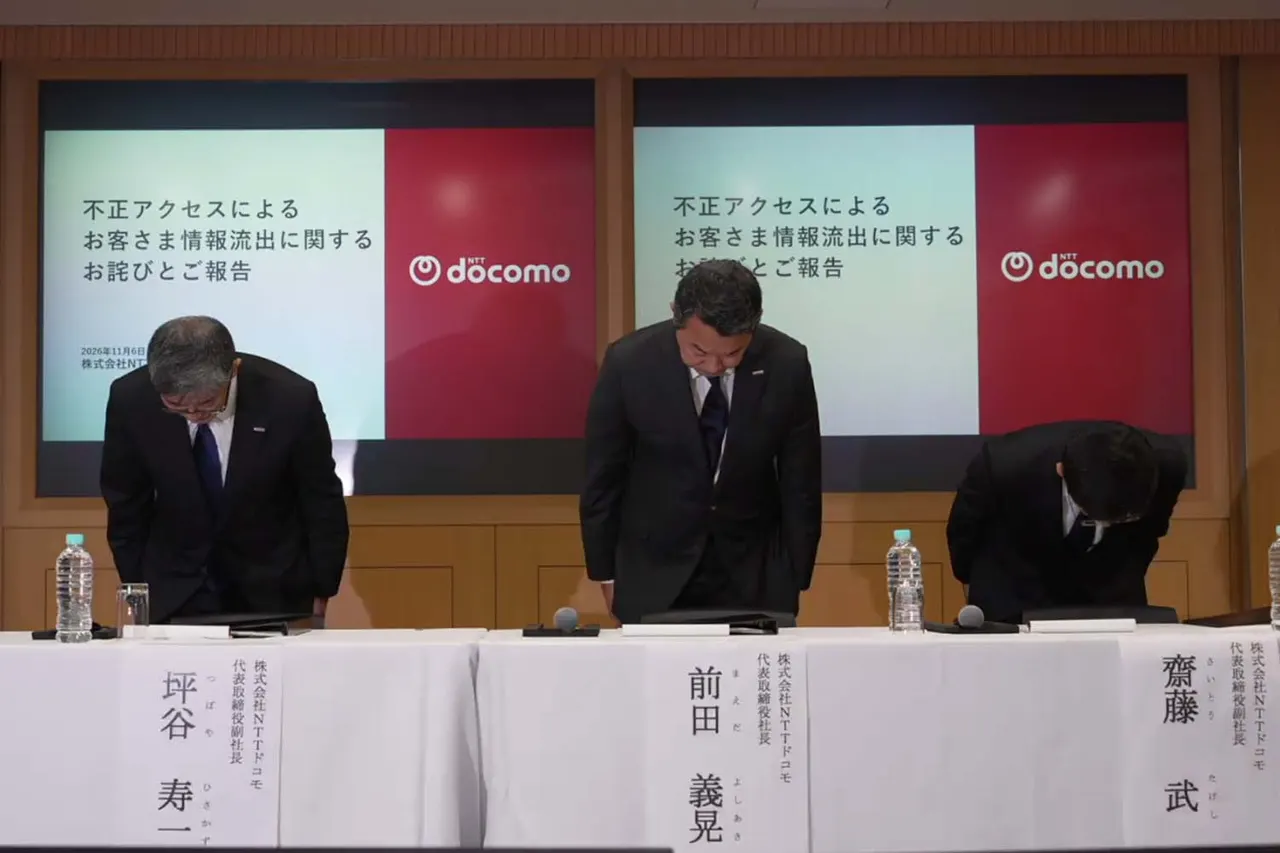
NTT Docomo has apologized for unauthorized access to My docomo and its online shop, saying the leak also covered ID document numbers and plan details for up to 294,839 lines.
 SUMO· the number puzzle
 Dialo· learn languages by speaking
 ediviewer· read EDI files like documents
 giftdetect· the right gift in minutes
NTT Docomo apologized at a press conference on 6 November over unauthorized access to its Docomo Online Shop and the My docomo member service, confirming that the leaked data is broader than first announced. The number of affected lines is up to 294,839: 204,157 individual and 90,682 corporate.
The company had already said on 5 November that names, addresses, dates of birth and mobile phone numbers might be affected. It now adds ID document numbers and rate plan and option details. For some users, the data also includes the names and contact details of legal or procedural representatives, company names and addresses, and financial institution names, branch names and account numbers.
How the attack unfolded
According to Docomo, an external attacker used the internet to exploit the way several linked systems interact, and searched for and retrieved user data automatically. The company detected a high-volume access alert at 10:30 on 4 November. Blocking overseas IP addresses at 14:30 had no effect, and My docomo went into maintenance mode at 16:20. After a specific attack route was cut, the service was restored at 20:32, but a further sign of unauthorized access led the company to take both My docomo and the online shop offline at 1:05 on 5 November. The leak was confirmed at 2:10.
Docomo says this was not a flaw in the systems themselves but an abuse of linked systems, a route that its regular vulnerability assessments had not identified. Vice President Juichi Tsuboya said it was not a so-called API attack, and the company is still checking whether AI agents were used. President Yoshiaki Maeda said: "We do not think we contained it early. 300,000 is a large number and the information is important. We take this seriously."
Response and a separate outage
Individual customers were sent an SMS on 6 November with an apology, an overview and safety advice, while corporate customers will be contacted by sales staff, SMS or direct mail. Docomo is considering condolence payments for both groups, with details to follow. Users are urged not to open URLs or attachments in suspicious emails or SMS messages.
The company also explained a 5G SA outage from about 11:18 on 5 November to about 1:20 on 6 November that affected up to roughly 1.587 million subscribers nationwide. A memory fault in part of the switching equipment, triggered by core network maintenance, caused processing delays and congestion. Emergency alerts and MVNOs on Docomo lines were unaffected. A temporary fix is in place, and a permanent measure is due within a week.
Apps worth a look
SUMO: the number puzzleTap the right tiles, add them up, hit the target. Easy to learn, hard to master. Free, for all ages.
Dialo: learn languages by speakingTalk to an AI conversation partner; every sentence comes back corrected and explained in your language. 9 languages, A1 to C2.
ediviewer: read EDI files like documentsOpen EDIFACT and X12 messages, see every segment explained, convert to JSON/XML, export PDF and Excel. Runs locally, no upload.
giftdetect: the right gift in minutesPick who it is for, the occasion and their personality. The search engine reads product descriptions from local shops and ranks what fits. Free, no sign-up.