Beget Confirms Cyberattack That Wiped Cloud Data and Backups
Russian hosting provider Beget says attackers reached its control layer and ran wiping scripts, destroying all cloud data across VPS, S3 and Kubernetes.
 SUMO· the number puzzle
 Dialo· learn languages by speaking
 ediviewer· read EDI files like documents
 giftdetect· the right gift in minutes
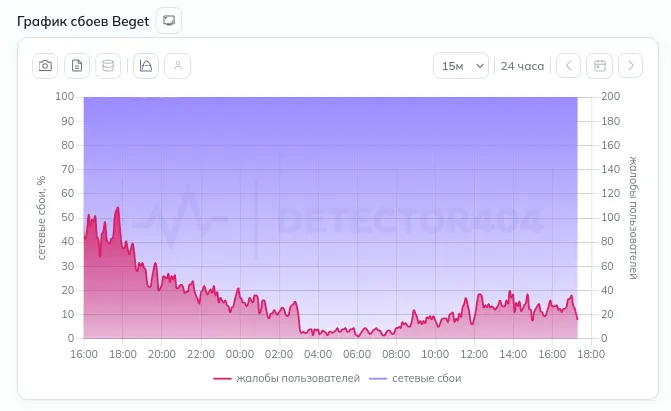
Russian hosting provider Beget has confirmed that its IT infrastructure was hit by a cyberattack overnight between 1 and 2 November 2026. According to the company, the attackers gained access to the control layer of the entire architecture and then launched scripts that wiped data.
The cloud platform took the heaviest blow. All data in the cloud infrastructure, covering VPS, S3 and Kubernetes, was lost, along with CDN and IP settings. Binary VPS backups are gone completely, but file-level backups of VPS survive. The company says file backups of the whole hosting and cloud estate are also intact, though it cannot yet give customers access to them. Every server must first be checked by hand for hidden vulnerabilities and malicious scripts.
What has been restored
Dedicated servers that customers administer themselves are back in service, and servers managed by Beget are being checked and returned gradually. Preliminary estimates suggest nearly 100% of sites on shared hosting can be recovered, but launching that service also requires careful checks. The mail service is 80% restored, with full operation expected within 10 hours.
DNS management is partly available. Customers can change A, MX and TXT records for domains in the .ru, .рф and .su zones through a separate page, domains.beget.ru, provided the domains are registered with Beget and use its DNS servers. International domains are still being worked on. Beget also says it has agreed with the Coordination Center for the Russian domain space that expiring domains in those zones will not be undelegated.
What customers should do
The company reports no attempts to download or modify user data on servers that held it, but advises changing all passwords, access keys and other credentials that may have been stored there. A limited control panel for some services is promised within 24 hours.
Beget has not given a recovery timeline, since more than 1,000 servers need manual inspection. It declined to disclose further details of the attack so as not to harm the investigation and the safe relaunch of its systems, and has declared force majeure.
Apps worth a look
SUMO: the number puzzleTap the right tiles, add them up, hit the target. Easy to learn, hard to master. Free, for all ages.
Dialo: learn languages by speakingTalk to an AI conversation partner; every sentence comes back corrected and explained in your language. 9 languages, A1 to C2.
ediviewer: read EDI files like documentsOpen EDIFACT and X12 messages, see every segment explained, convert to JSON/XML, export PDF and Excel. Runs locally, no upload.
giftdetect: the right gift in minutesPick who it is for, the occasion and their personality. The search engine reads product descriptions from local shops and ranks what fits. Free, no sign-up.
More from this day
See all →Return secures €835 million to expand battery storage in Germany
Traversal raises $120M at a $1B valuation for AI reliability agent
fal raises $1.3 billion at a $16 billion valuation
OneStack raises Rs 12.5 crore led by Shepherd's Hill
More in: Security
See all →
I4C warns banks and fintechs of AI agent-driven fraud attacks

Google Warns of LLMjacking: $100,000 in Fraudulent Use in a Day

Japan's e-Tax Goes Into Emergency Maintenance After Suspicious Traffic
