Arara Message Breach: 77 Million Email Addresses at Risk
Japan's Arara says a breach of its Arara Message email service may have exposed about 77 million email addresses from up to 380 client companies. The service is fully suspended.
Arara, a Tokyo-based subsidiary of PayCloud Holdings, says roughly 77 million additional email addresses have been leaked or may have been exposed in an unauthorized access incident affecting its email delivery service Arara Message. Up to about 380 client companies are affected, according to an update announced on November 2. The service has been fully suspended since October 31, and no restart date has been set.
Attackers moved from shared environment to client systems
On October 29, the company had disclosed that about 3.01 million email addresses were leaked after attackers breached a shared system environment. Further investigation showed the damage had spread to other servers.
Between October 28 and 31, the attacker reached client companies' own system environments via Arara Message servers and took email addresses and member data from 97 servers. The data includes names, gender, dates of birth, phone numbers, member IDs and addresses, depending on the client. The figure is still being verified and may change. Because one person can hold several addresses, it does not equal the number of victims.
The earlier incident count was also revised upward, from about 3.01 million to 3,386,187 email addresses. Customer data from five client companies, including names and company names, may also have leaked, up to 411,827 records. These figures may overlap with the 77 million and were not added together.
Phishing emails sent through the service
The attacker also abused the service to send up to about 7.13 million emails posing as a credit card company between October 28 and 30. They came from news@arara.com, with subjects such as requests to confirm card usage or statements. The company urges recipients not to click any URLs in them.
The company says web server vulnerabilities and problems in the system environment were involved. It has disabled the misused credentials and cut server communications. It plans to identify the intrusion route and confirm security before deciding on a restart. Other Arara services are not affected.
Separately, leisure booking service Asoview said on November 3 that 15,821,184 member records were leaked through the same incident, including email addresses, names, phone numbers, ticket purchase dates and facility names. Passwords and credit card data were not included.
Apps worth a look
 SUMO: the number puzzle
Tap the right tiles, add them up, hit the target. Easy to learn, hard to master. Free, for all ages.
 Dialo: learn languages by speaking
Talk to an AI conversation partner; every sentence comes back corrected and explained in your language. 9 languages, A1 to C2.
 ediviewer: read EDI files like documents
Open EDIFACT and X12 messages, see every segment explained, convert to JSON/XML, export PDF and Excel. Runs locally, no upload.
More from this day
See all →
OpenAI to retire ChatGPT Classic desktop app on January 30, 2027
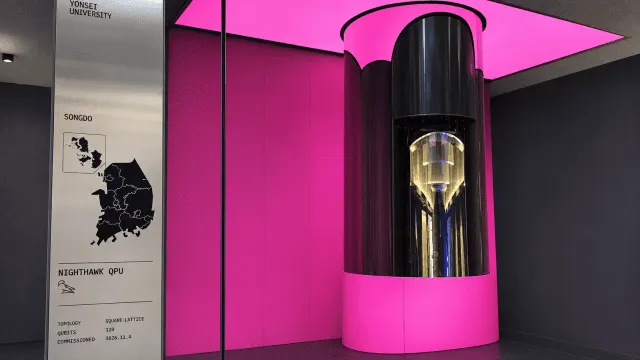
Yonsei University Switches On IBM Quantum Nighthawk r2 System
KakaoBank Eyes Cards and Brokerage, Plans 2028 Business Banking
T map Sale to Goldman Sachs Cannot Send User Data Abroad
More in: Security
See all →
Beget Loses Cloud Data After Cyberattack on Its Infrastructure
VOLTA malware steals passwords and asks AI what victims are worth
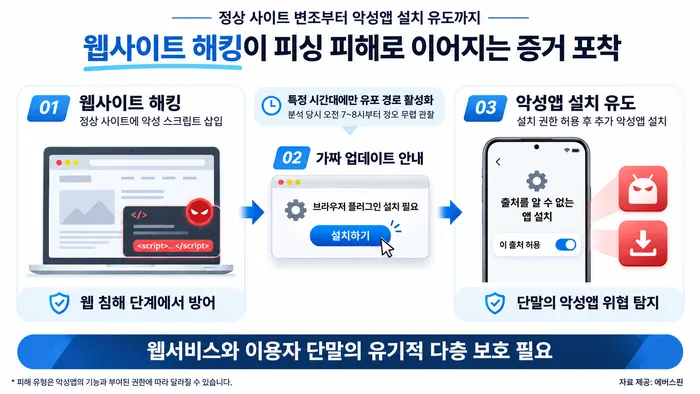
Fake Samsung Browser Update on Hacked Sites Spreads Android Malware