Korea's Financial Security Institute Hit by Data Leak Ahead of Conference
A hack of the Financial Security Institute's assessment system leaked data submitted by financial firms, putting the agency's security skills and its director under scrutiny.
 SUMO· the number puzzle
 Dialo· learn languages by speaking
 ediviewer· read EDI files like documents
 giftdetect· the right gift in minutes
South Korea's Financial Security Institute, funded by member fees from financial firms, has leaked materials those firms submitted to it after a hack. The breach has raised questions about the agency's own security capabilities and about how far its remit now extends.
The compromised system is the "continuous information security assessment support system", where financial companies upload materials so their security management can be evaluated. In other words, the body that grades the sector's protection levels lost data it was holding for that very purpose.
A body built to defend the sector
The institute was launched in 2015 by merging the information sharing and analysis centers of the Korea Financial Telecommunications and Clearings Institute and Koscom with the Financial Security Research Institute. The aim was to bring security monitoring, incident response and vulnerability analysis under one roof, for threats individual firms struggle to handle alone.
Since then it has expanded beyond security, blurring the line between its role and those of related bodies such as the Korea Credit Information Services and the clearings institute. The Financial Data Exchange it opened in 2020 is a prime example. Data provided by a Democratic Party lawmaker's office shows it recorded just three paid transactions worth 14.98 million won in 2024.
Questions over leadership
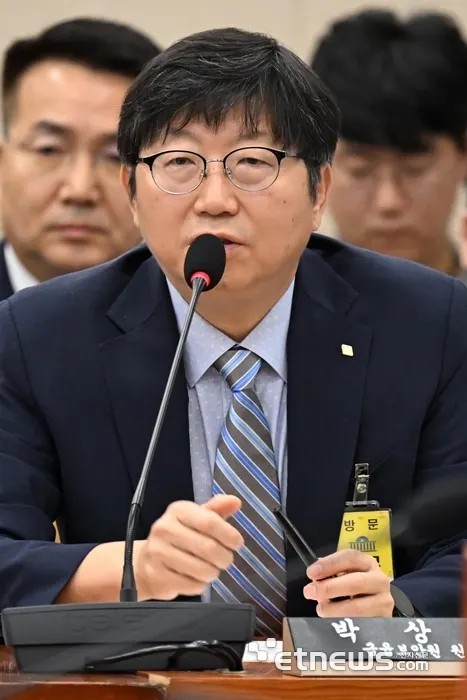
Director Park Sang-won has also come under fire. He previously handled financial group supervision, planning and management, and small-business and consumer finance at the Financial Supervisory Service, but has no hands-on experience in cybersecurity or incident response. Critics say that makes it hard to defend his ability to lead the agency's core work, and some argue he bears responsibility for managing internal security risk.
The timing adds pressure. The institute is holding its financial information security conference, PISCON 2026, on the 12th in Yeouido, Seoul, under the theme "Today's Strategy for Tomorrow's Finance", to discuss AI-era cyber threats. The leak came three days before the event.
An industry source said attention is on whether the institute will apologize at the conference and explain how the leak happened and how it will prevent a repeat. Because the financial authorities, financial institutions and the affected firms have all been invited, the source said it should explain accountability before talking about future security strategy.
Apps worth a look
SUMO: the number puzzleTap the right tiles, add them up, hit the target. Easy to learn, hard to master. Free, for all ages.
Dialo: learn languages by speakingTalk to an AI conversation partner; every sentence comes back corrected and explained in your language. 9 languages, A1 to C2.
ediviewer: read EDI files like documentsOpen EDIFACT and X12 messages, see every segment explained, convert to JSON/XML, export PDF and Excel. Runs locally, no upload.
giftdetect: the right gift in minutesPick who it is for, the occasion and their personality. The search engine reads product descriptions from local shops and ranks what fits. Free, no sign-up.
More from this day
See all →
Google Wallet Adds Digital Home Keys for NFC and UWB Smart Locks

TSMC plans up to $1 billion investment in Anthropic and OpenAI

Acecore, Supplya and Navidyn Take Top Spots at TC Battlefield

Airwallex to invest more than $1.6 billion in Singapore over five years
More in: Security
See all →
Yasukuni Shrine Online Shop Breach Exposes 14,500 Records

GMO Aozora Net Bank Halts Banking API Twice After Attacks

Helix Replaces Captchas With a Four-Digit Voice Check
