HYBE Confirms Data Breach Hitting Former Staff and Partners
HYBE says attackers accessed internal documents through a document preview tool tied to its e-approval system, exposing personal data of former staff and partner contacts.
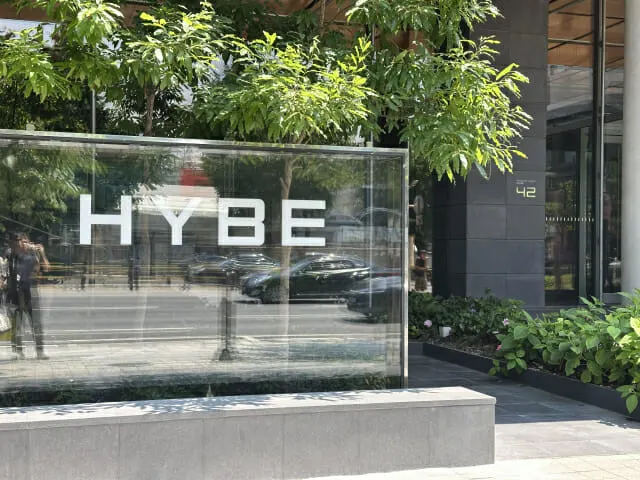
HYBE has confirmed that personal data belonging to former employees and staff at partner companies was leaked from its internal systems. According to a notice the company posted on its official website on October 18, the incident was found during an internal security check.
The company said it detected signs of abnormal external access to a third-party document preview solution connected to its electronic approval system. Its investigation found that some internal documents stored on the e-approval server and the expense-processing system, along with the personal information inside them, were taken.
What was exposed
The affected data items include names, resident registration numbers, foreign registration numbers, passport numbers, bank account numbers, card numbers, mobile and phone numbers, email addresses, home addresses, medical information, dates of birth, IP addresses, employee IDs and department names. HYBE said the leaked information covered some personal data of partner-company contacts and former members of staff.
The unauthorized access occurred in two windows: from 1:16 p.m. on September 12 to 11:14 a.m. on September 13, and from 10:41 p.m. on October 3 to 3:05 p.m. on October 5.
Response and advice
HYBE said it has fully blocked the IP addresses and access route used in the attack and urgently suspended the preview service to stop further leakage. It has reported the incident to the Korea Internet & Security Agency (KISA) and the Personal Information Protection Commission, as required by law, and will notify affected individuals directly.
The company said it has not received reports of the data being misused so far. To limit secondary harm, it urged people not to respond to messages that impersonate HYBE departments or employees and ask for account details, money or sensitive materials. It also noted that those who suffered losses can seek statutory damages and may apply for mediation with the Personal Information Dispute Mediation Committee.
Apps worth a look
 SUMO: the number puzzle
Tap the right tiles, add them up, hit the target. Easy to learn, hard to master. Free, for all ages.
 Dialo: learn languages by speaking
Talk to an AI conversation partner; every sentence comes back corrected and explained in your language. 9 languages, A1 to C2.
 ediviewer: read EDI files like documents
Open EDIFACT and X12 messages, see every segment explained, convert to JSON/XML, export PDF and Excel. Runs locally, no upload.