Fugaku supercomputer hacked via public dashboard, now offline
Japan's Fugaku supercomputer has been shut down after an intruder got in through a public status dashboard. SSH keys and research files of up to 4,222 users may have leaked.
 SUMO· the number puzzle
 Dialo· learn languages by speaking
 ediviewer· read EDI files like documents
 giftdetect· the right gift in minutes
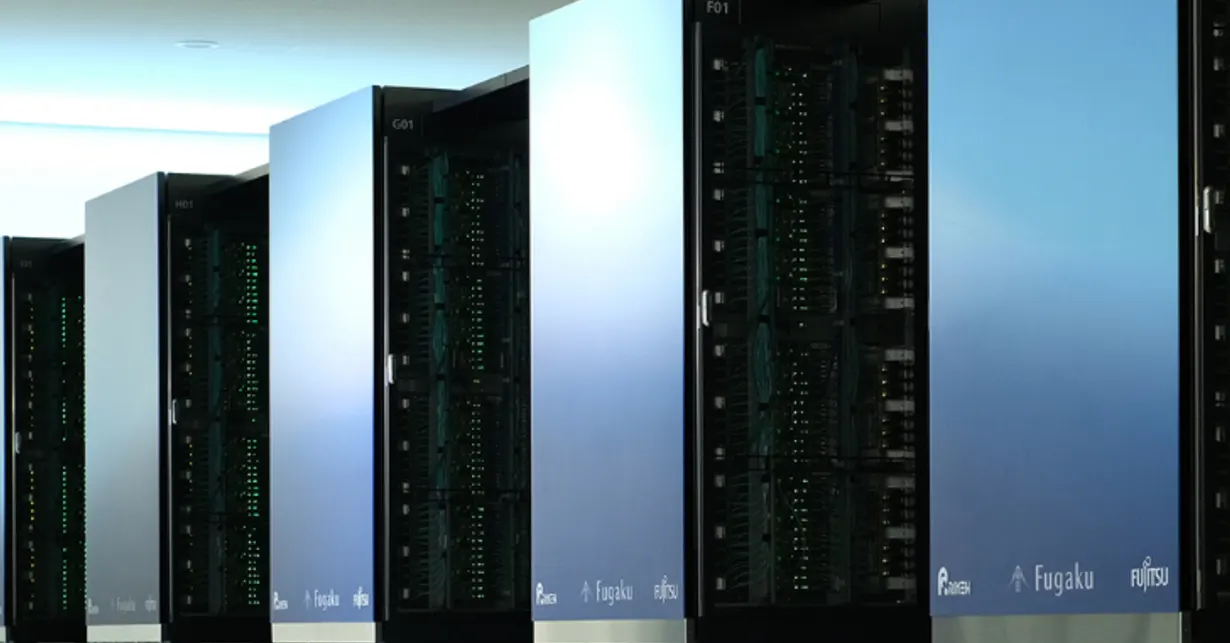
The Fugaku supercomputer, one of Japan's flagship research machines, has been switched off after an intruder got into its internal network through a web page that was meant to show how busy the system was.
RIKEN, the research institute that runs it, said on 16 November that an outside party accessed the operational systems of Fugaku at its Center for Computational Science. Operations were halted in the early hours of 14 November. The dashboard, a public page showing Fugaku's operating status, was the foothold. How exactly the attacker used it is still under investigation.
What was taken in the Fugaku breach?
Between 10 and 13 November the intruder operated several internal servers and planted malicious programs on some of them. RIKEN says data may have been taken from the authentication system: names, email addresses and IDs of up to 4,222 Fugaku users, plus names and email addresses of up to 375 users of Riku-kyu ("Rikyu"), an AI-focused science supercomputer.
The worrying part is what users keep in their home directories. SSH private keys, access keys and research files may also have been copied. The attacker used some of the stolen credentials to try to connect to other systems. RIKEN has found no concrete sign that research results leaked, and is working with other organisations to check for secondary damage.
How did RIKEN respond?
RIKEN noticed suspicious traffic on 12 November, and its outsourced maintenance contractor started investigating. The breach was confirmed on 13 November and the affected system was isolated. Fugaku went down on 14 November and admin keys were swapped the same day. On the evening of 15 November all running and queued jobs were stopped, and every user's login public key was invalidated.
Users are asked to revoke any SSH keys and credentials stored on Fugaku and issue new ones. RIKEN will patch the exploited software flaw, rebuild the compromised servers, redesign the network and add AI-based security measures. Fugaku will return only after those fixes, and the maintenance team's roles will be reshuffled so emergencies get a faster response.
Apps worth a look
SUMO: the number puzzleTap the right tiles, add them up, hit the target. Easy to learn, hard to master. Free, for all ages.
Dialo: learn languages by speakingTalk to an AI conversation partner; every sentence comes back corrected and explained in your language. 9 languages, A1 to C2.
ediviewer: read EDI files like documentsOpen EDIFACT and X12 messages, see every segment explained, convert to JSON/XML, export PDF and Excel. Runs locally, no upload.
giftdetect: the right gift in minutesPick who it is for, the occasion and their personality. The search engine reads product descriptions from local shops and ranks what fits. Free, no sign-up.