ARTEX: the AI hacking framework behind attacks on banks and clouds
Attackers are using the open source ARTEX framework to run AI agents that steal API keys and fake live selfie checks. Some intrusions took under three hours, the FBI says.

 SUMO· the number puzzle
 Dialo· learn languages by speaking
 ediviewer· read EDI files like documents
 giftdetect· the right gift in minutes
ARTEX started life as an open source AI penetration testing tool. Now the FBI and Amazon Threat Intelligence say attackers are using it to run armies of AI agents against banks, governments, energy firms and healthcare providers.
Between October 3 and November 5, Amazon's MadPot honeypot sensors (decoy systems that attract attackers) spotted two ARTEX campaigns. In the first, agents stole API keys and fed them into ARTEX's model gateway, which then powered more agents hunting for more keys. The aim was free access to AI models, at what Amazon calls "industrial scale". Targets included LLM gateways such as LiteLLM and One API, and app builders such as Dify, Langflow, Open WebUI and Ollama.
The second campaign went after identity checks at two cryptocurrency exchanges. Agents built a real-time deepfake video pipeline on a single consumer-grade GPU, reaching 11.5 frames per second, and forged ID photos with matching camera metadata. The deepfake even hit its movement targets to within 7 pixels. It still failed: the vendor's server-side check rejected it every time.
How dangerous is ARTEX?
None of the techniques are new. The speed is. The FBI says some intrusions went from first targeting to privileged access in under three hours. It cited August attacks on South Korean financial institutions that exposed data on about 67,000 people, and a September supply chain attack on ConnectWise Cloud Backup customers that compromised more than 2,250 downstream Microsoft tenants.
The original developer pulled the GitHub repository in October, but forks, localized versions and a commercial edition remain. Censys found 1,465 hosts with an exposed ARTEX console on November 4, and the FBI believes the real number is significantly higher.
How to defend against AI agent attacks
AWS security chief CJ Moses says the agents won over weak basics: default or hardcoded credentials, keys left in code, unauthenticated interfaces and unpatched software. The FBI advises shrinking external attack surfaces, keeping sensitive services on trusted networks or private connections, and putting enterprise apps behind zero-trust access policies.
Apps worth a look
SUMO: the number puzzleTap the right tiles, add them up, hit the target. Easy to learn, hard to master. Free, for all ages.
Dialo: learn languages by speakingTalk to an AI conversation partner; every sentence comes back corrected and explained in your language. 9 languages, A1 to C2.
ediviewer: read EDI files like documentsOpen EDIFACT and X12 messages, see every segment explained, convert to JSON/XML, export PDF and Excel. Runs locally, no upload.
giftdetect: the right gift in minutesPick who it is for, the occasion and their personality. The search engine reads product descriptions from local shops and ranks what fits. Free, no sign-up.
More from this day
See all →
FAA router grounding: FBI takes the suspect router into custody
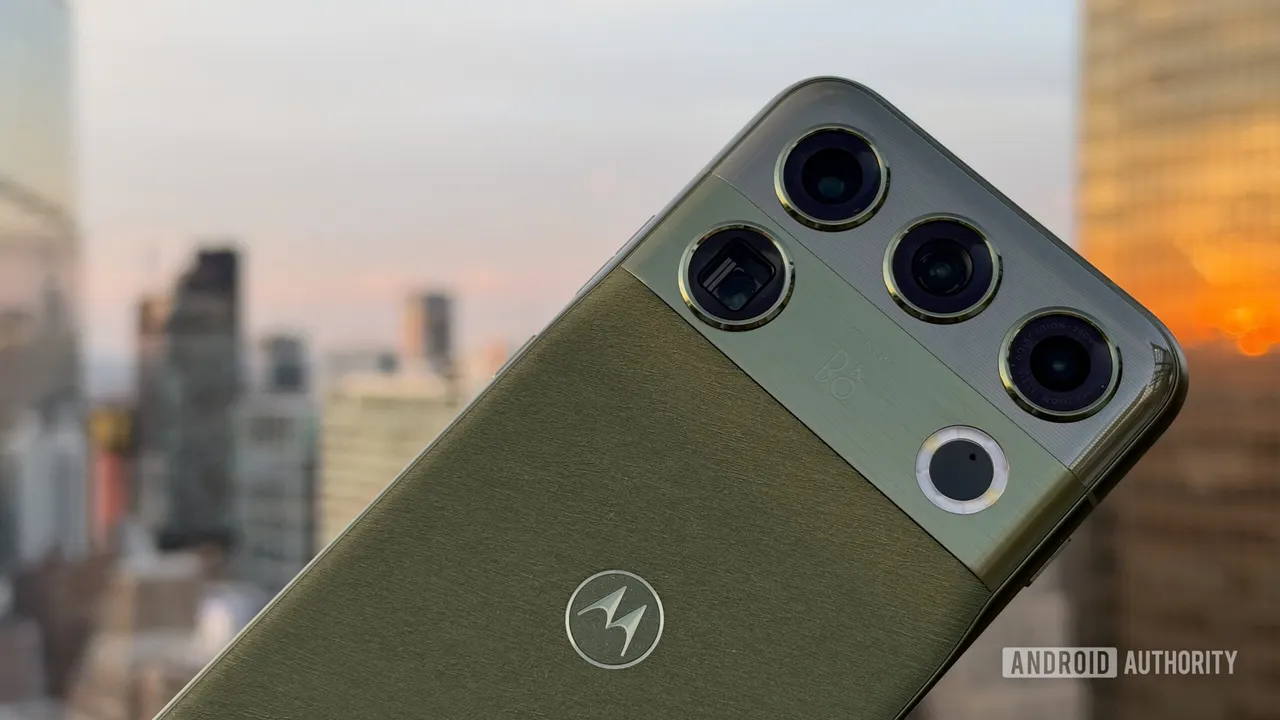
Motorola Signature 27 in Germany gets a smaller 5,500mAh battery
Claude Code's settings.local.json put passwords on GitHub