Apple to Scan Public iCloud Links for Harmful Content in iOS 27.3
With iOS 27.3, Apple will review iCloud items shared via 'Anyone with the link' and may delete content or disable accounts. 'Harmful' is not defined.
 SUMO· the number puzzle
 Dialo· learn languages by speaking
 ediviewer· read EDI files like documents
 giftdetect· the right gift in minutes
Apple will start reviewing iCloud items shared through public links, and it reserves the right to remove content or disable the accounts behind it. The policy comes with the first iOS 27.3 beta, which reached developers during the week of 3 November, along with a support page published the same day.
According to that page, items shared via iCloud with the "Anyone with the link" option will be "checked by Apple for harmful content". The rule applies from version 27.3 of iOS, iPadOS, macOS and visionOS, with final releases expected in December.
What is covered, and what is not
The option turns a photo from iCloud Photos or a file from iCloud Drive into an open link that anyone can view without an invitation or an account. Apple states plainly that such content is accessible to anyone with the address, "including Apple". The beta also adds a new warning when you create such a link, still shown in English in this first build.
The page also notes that an item shared this way is "no longer end-to-end encrypted, even if the owner or participants have enabled Advanced Data Protection". That rule predates the update. Sharing restricted to "people you choose", by invitation or approval, and sending a copy of a file fall outside the described scope.
Sanctions and open questions
Apple says it may "move, reject, edit, remove or delete content at any time". Penalties can extend to blocking or disabling the account, with a ban on opening a new one using the same email address or phone number. Law enforcement may be contacted "if necessary". The page describes no notification to the owner and no appeal process.
The word "harmful" is not defined. The page names no categories, no review method, whether human or automated, and does not say what happens to links created before the update. Apple has not clarified anything since publication. iCloud terms already prohibited illegal content, but the page now announces a formal check.
The move recalls Apple's 2021 plan to detect child sexual abuse imagery in iCloud photo libraries, which it dropped on 7 December 2022 under pressure from privacy advocates. A class action seeking up to $32.8 billion had faulted the company for inaction; a federal judge dismissed it in July under Section 230. This time, inspection is limited to public shares.
Apps worth a look
SUMO: the number puzzleTap the right tiles, add them up, hit the target. Easy to learn, hard to master. Free, for all ages.
Dialo: learn languages by speakingTalk to an AI conversation partner; every sentence comes back corrected and explained in your language. 9 languages, A1 to C2.
ediviewer: read EDI files like documentsOpen EDIFACT and X12 messages, see every segment explained, convert to JSON/XML, export PDF and Excel. Runs locally, no upload.
giftdetect: the right gift in minutesPick who it is for, the occasion and their personality. The search engine reads product descriptions from local shops and ranks what fits. Free, no sign-up.
More from this day
See all →
Google plans $15 billion Malaysia data center push for AI demand
Heidi Health to cut 18% of staff after US$140 million round
Early Revolut employees launch AI wealthtech Haido from stealth
Kabilio raises €10 million for its AI accounting agent in Barcelona
More in: Security
See all →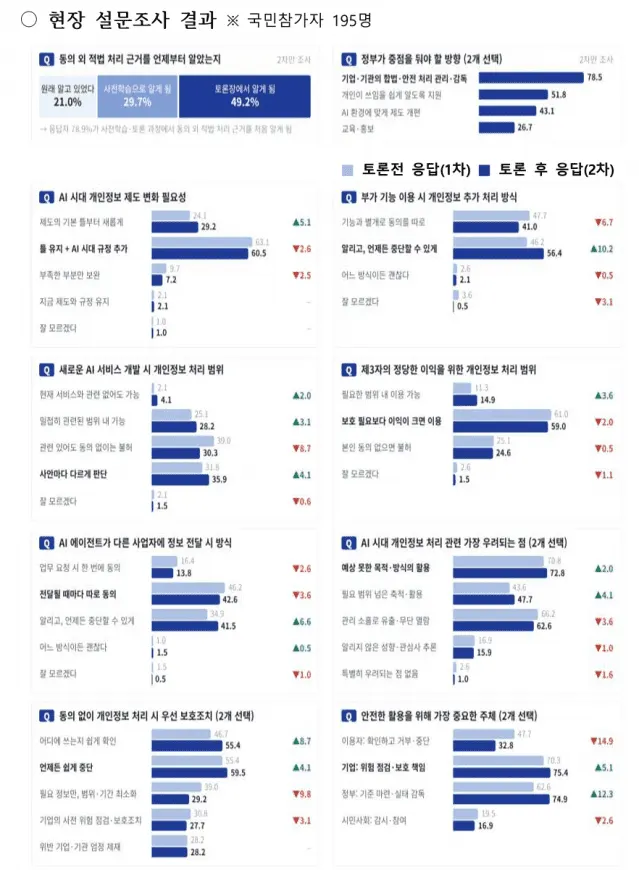
South Korea's PIPC to Overhaul Privacy Rules for AI by Year-End
NIKKE PC Launcher Hit by Tampered CDN Scripts, Malware Risk