Optimizely hack: malicious script hit BBC, Ikea and Zoom sites
Attackers didn't touch the BBC or Ikea directly. They hacked Optimizely, an A/B testing vendor, and its own trusted server delivered card-stealing code for 17 hours.

 SUMO· the number puzzle
 Dialo· learn languages by speaking
 ediviewer· read EDI files like documents
 giftdetect· the right gift in minutes
The Optimizely hack shows how you can attack the BBC, Ikea or Zoom without going near their servers. The attackers went after a supplier instead, and the supplier's own trusted server did the rest.
On Monday 16 November, Optimizely, a company that runs A/B tests for other businesses, was compromised. According to Optimizely, the attackers injected malicious code by exploiting a flaw in its account sign-up process. That code then travelled to the websites of customers using the testing service. The attack lasted about 17 hours, and at first nobody noticed.
The code reached sites including the BBC, Ikea, CNN, Fox News, Zoom and Air France-KLM. It could steal bank card data, load exploits aimed at iPhones and iPads that hadn't been updated, and swap the addresses of crypto wallets. Scott Helme of Report URI spotted it. He analysed 1,611 Optimizely scripts and found 188 infected ones, belonging to 178 organisations.
What is Optimizely and why did the browser trust it?
Optimizely sells A/B testing: show half of visitors a green button and half a blue one, and keep whichever gets more clicks. Customers load a small script on every visit, and it includes a field where they add their own code. That lets them change a site without touching their own servers. It is also exactly where the attackers got in.
The malicious script came from cdn.optimizely.com, the company's official server, with a valid certificate. To a browser, it looked genuine.
How much was stolen?
Preliminary data from Report URI suggests the attacker's wallets received around $7,000 in crypto, although some of them were active before the attack. There is no evidence that any iPhone or iPad was actually compromised, and nobody knows how many cards or cookies were taken.
Optimizely hasn't yet explained how the flaw worked, how many visitors received the code, or who is behind it. It also confirmed an intrusion in February, after a phone phishing attack. For a company whose product lives inside its customers' websites, that is a lot of open questions.
Apps worth a look
SUMO: the number puzzleTap the right tiles, add them up, hit the target. Easy to learn, hard to master. Free, for all ages.
Dialo: learn languages by speakingTalk to an AI conversation partner; every sentence comes back corrected and explained in your language. 9 languages, A1 to C2.
ediviewer: read EDI files like documentsOpen EDIFACT and X12 messages, see every segment explained, convert to JSON/XML, export PDF and Excel. Runs locally, no upload.
giftdetect: the right gift in minutesPick who it is for, the occasion and their personality. The search engine reads product descriptions from local shops and ranks what fits. Free, no sign-up.
More from this day
See all →
Windows 11 Emerging Risks will warn you about risky apps and drivers
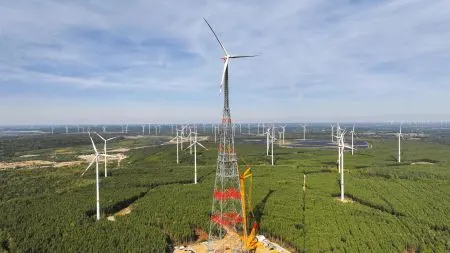
World's tallest wind turbine now feeds power in Schipkau
Supernova SN 2026ahvu: caught early, with a puzzle attached