Nitori Warns Up to 37.62 Million Records May Have Leaked
Nitori Holdings says unauthorized access may have exposed personal data of up to 37.62 million records, including names, addresses and order details. Card data was not affected.
 SUMO· the number puzzle
 Dialo· learn languages by speaking
 ediviewer· read EDI files like documents
 giftdetect· the right gift in minutes
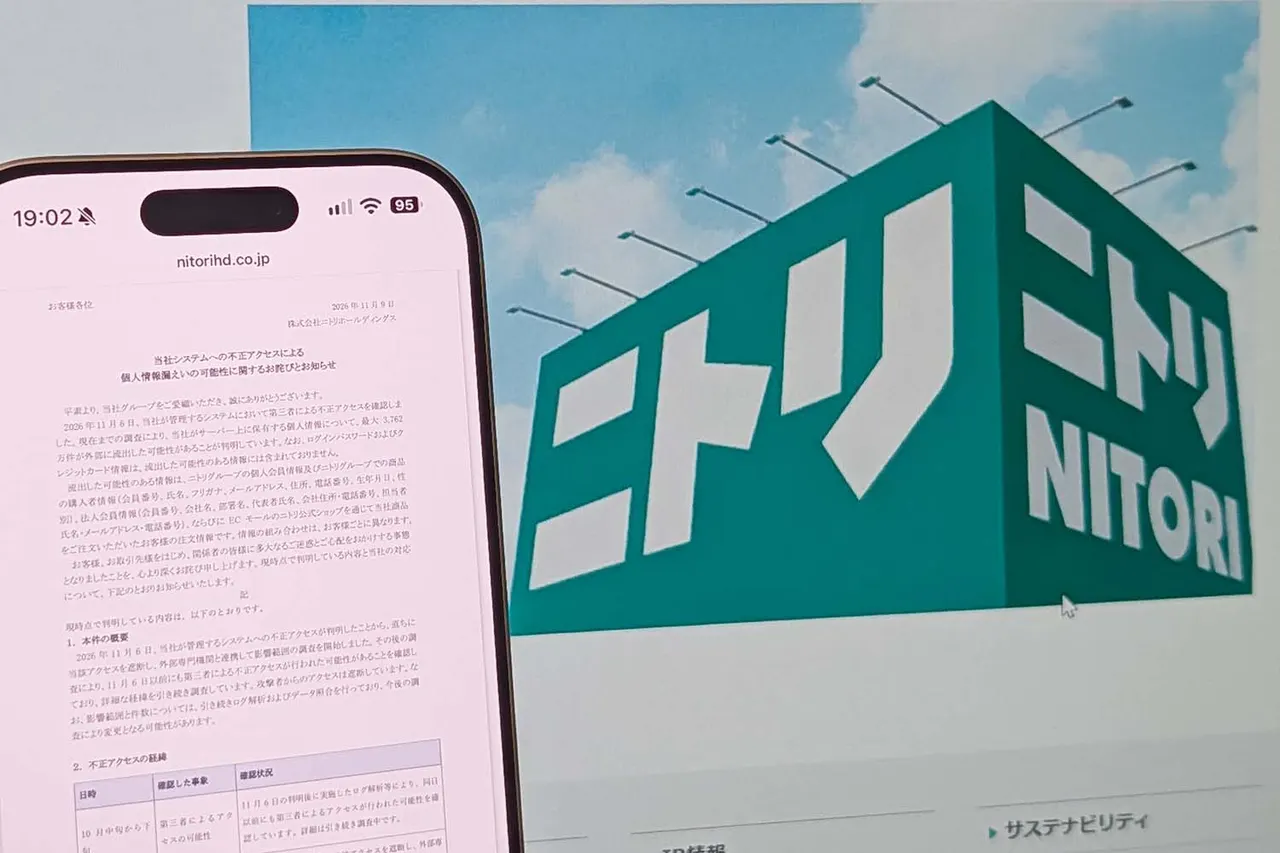
Nitori Holdings announced on 9 November that a third party's unauthorized access to its systems may have leaked as many as 37.62 million personal data records.
The company says the potentially exposed data covers individual members of the Nitori Group and people who bought products from the group. That includes member numbers, names, name readings in kana, email addresses, postal addresses, phone numbers, dates of birth and gender. Corporate member records may also be affected, with member numbers, company and department names, representative names, company addresses and phone numbers, and contact persons' names, email addresses and phone numbers. Order information from people who purchased through Nitori Net and the official Nitori shops is included as well. The combination of data differs from user to user.
Nitori states that credit card information and login passwords are not part of the leak.
Timeline and investigation
The company discovered the unauthorized access on 6 November and cut it off immediately. It then began assessing the impact together with external specialists. That work found that unauthorized access may also have occurred before that date, from mid to late October. Nitori says it is still verifying the details.
What customers should do
Because the data could be abused, Nitori Holdings warns of spoofed emails, phishing scams and suspicious phone calls. It urges customers to be cautious about messages that claim to come from Nitori, delivery companies or e-commerce marketplaces, and not to open links or attachments they do not recognize.
The scale makes this one of the larger personal data incidents reported by a Japanese retailer, and the mix of contact details, birth dates and purchase history is the kind of information commonly used to make phishing messages look convincing. The company has not yet said when its investigation will conclude.
Apps worth a look
SUMO: the number puzzleTap the right tiles, add them up, hit the target. Easy to learn, hard to master. Free, for all ages.
Dialo: learn languages by speakingTalk to an AI conversation partner; every sentence comes back corrected and explained in your language. 9 languages, A1 to C2.
ediviewer: read EDI files like documentsOpen EDIFACT and X12 messages, see every segment explained, convert to JSON/XML, export PDF and Excel. Runs locally, no upload.
giftdetect: the right gift in minutesPick who it is for, the occasion and their personality. The search engine reads product descriptions from local shops and ranks what fits. Free, no sign-up.
More from this day
See all →
Budimex Tests Autonomous Rollers as Poland's Labor Shortage Bites
Android Auto Ends Support for Phones Running Android 9 and 10

FBI and CISA Warn Hackers Are Targeting Industrial Fridges Worldwide