Malicious Claude Code 2.1.313 Extension Planted an SSH Backdoor
A tampered Claude Code extension, version 2.1.313, spread via Open VSX and the Cursor marketplace and tried to install an SSH backdoor on macOS, Linux and Windows.
A compromised version of the official Claude Code extension for VS Code was distributed through the Open VSX registry and the Cursor marketplace, and it tried to install a persistent SSH backdoor on developer machines running macOS, Linux and Windows. The affected build is version 2.1.313.
Security researchers at Phorion were the first to spot suspicious activity on endpoints. They urged organizations to check their environments for the extension version 2.1.313 and, if they find it, to start incident response. The build never appeared in the official Microsoft Visual Studio Marketplace. Anthropic has since replaced it with version 2.1.314, and an independent check found no malicious code in the new release.
What the malware did
According to Cursor, which confirmed the incident and said no more than 5,000 users were affected, the extension collected the host name, user name, operating system, architecture, home directory path, environment variable names, working directories, the configured Git email and the public IP address.
It then tried to add an attacker-controlled key to authorized_keys, enable the local SSH service and open a reverse SSH tunnel. Because of bugs in the malicious code, this step usually failed, except in rare cases where Cursor ran with administrator rights. The code also tried to keep the tunnel alive using a LaunchAgent on macOS or a scheduled task on Windows, retrying about every 60 seconds, and sent status data via an HTTP POST to a /beacon endpoint on port 8099.
Cursor says it removed the extension, temporarily shut down its VS Code marketplace, audited access and found no other compromised extensions, rotated keys, rebuilt the marketplace and, with the hosting provider, took the malicious server offline.
What users should do
Updating to 2.1.314 does not remove a backdoor that is already installed or undo earlier activity, so affected developers need to inspect their systems manually. Cursor said the build was not developed by Anthropic, yet it was uploaded through Anthropic's verified account, which points to a supply chain attack rather than intentional code from the company. The malicious version was reportedly pulled without notifying customers.
The incident comes shortly after Claude Code v2.1.311 added an environment variable that lets the AI agent delete files without asking for confirmation.
More from this day
See all →
France's Assembly Backs 5.5-Cent Per-Gigabyte Tax on Streaming
Korea Venture Business Association Picks Cobot System, Zens, Fitin
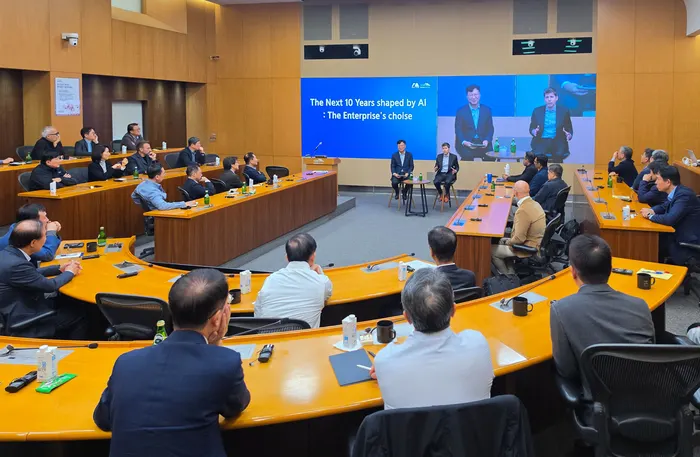
Samsung Invites OpenAI's Sam Altman to Brief Its Top Executives
LG Electronics Starts Building Its Cloid Humanoid In-House
More in: Security
See all →
Matsuya Foods Confirms Breach of 2.38 Million App Records

K2 Cybersecurity SOC Team Takes Second Place at GIS Days 2026

AO3 Goes Offline for Up to 4 Weeks After Security Incident
