Cyberattack Alters Blood Storage Freezers at French Facilities
Hackers changed temperature settings on refrigeration units at three French blood storage sites on 2 November. The EFS says no products were lost and no health risk arose.
 SUMO· the number puzzle
 Dialo· learn languages by speaking
 ediviewer· read EDI files like documents
 giftdetect· the right gift in minutes
A cyberattack tampered with refrigeration equipment used to store blood in France, the national blood service has confirmed. The Établissement Français du Sang (EFS), which collects, processes and distributes blood across the country, said the incident took place on 2 November.
Attackers changed temperature and defrosting parameters at three facilities that hold blood products. These sites store the reserves destined for hospitals as well as biological samples that must be kept under controlled conditions. According to the EFS, no products were lost and there was no risk to health.
The agency said the target was one of its refrigeration equipment suppliers, not the EFS itself. It did not name the company, but the European firm Coolworld Rentals acknowledged it was hit. In a brief statement, it said the hackers exploited a flaw in a third-party component to compromise its refrigeration units. The company added that no blood or plasma was lost and that collection and distribution carried on without interruption.
A wider pattern across Europe
The incident comes days after hackers breached hundreds of French supermarkets and stores in the Netherlands, where refrigeration failures reportedly spoiled tons of food. No group has claimed responsibility for any of the attacks on cooling systems. Agencies including France's ANSSI, Sweden's National Cyber Security Centre and Belgium's Federal Prosecutor's Office are investigating, but have not identified who is behind them.
In most cases, attackers exploit outdated remote modules and controllers, notably from Danfoss, Copeland and Dixell. These devices were connected to the internet without the necessary software updates. Weak access credentials and remote access to systems that no longer receive security patches add to the risk.
In 2025, the US Cybersecurity and Infrastructure Security Agency (CISA) disclosed two vulnerabilities in Danfoss controllers that could allow remote command execution and authentication bypass. Danfoss fixed the flaws and urged customers to update to the latest firmware, a step many of the affected refrigeration operators apparently skipped.
The pattern shows how everyday cold-chain equipment has become a target for attackers, with consequences that extend from food waste to medical supplies. Predicting the next target is difficult, particularly as AI helps uncover vulnerabilities before vendors can patch them.
Apps worth a look
SUMO: the number puzzleTap the right tiles, add them up, hit the target. Easy to learn, hard to master. Free, for all ages.
Dialo: learn languages by speakingTalk to an AI conversation partner; every sentence comes back corrected and explained in your language. 9 languages, A1 to C2.
ediviewer: read EDI files like documentsOpen EDIFACT and X12 messages, see every segment explained, convert to JSON/XML, export PDF and Excel. Runs locally, no upload.
giftdetect: the right gift in minutesPick who it is for, the occasion and their personality. The search engine reads product descriptions from local shops and ranks what fits. Free, no sign-up.
More from this day
See all →
Bic Camera Group: 14.9 Million Email Addresses May Have Leaked

Beget Restores 35% of Servers After Cyberattack Wiped Cloud Data
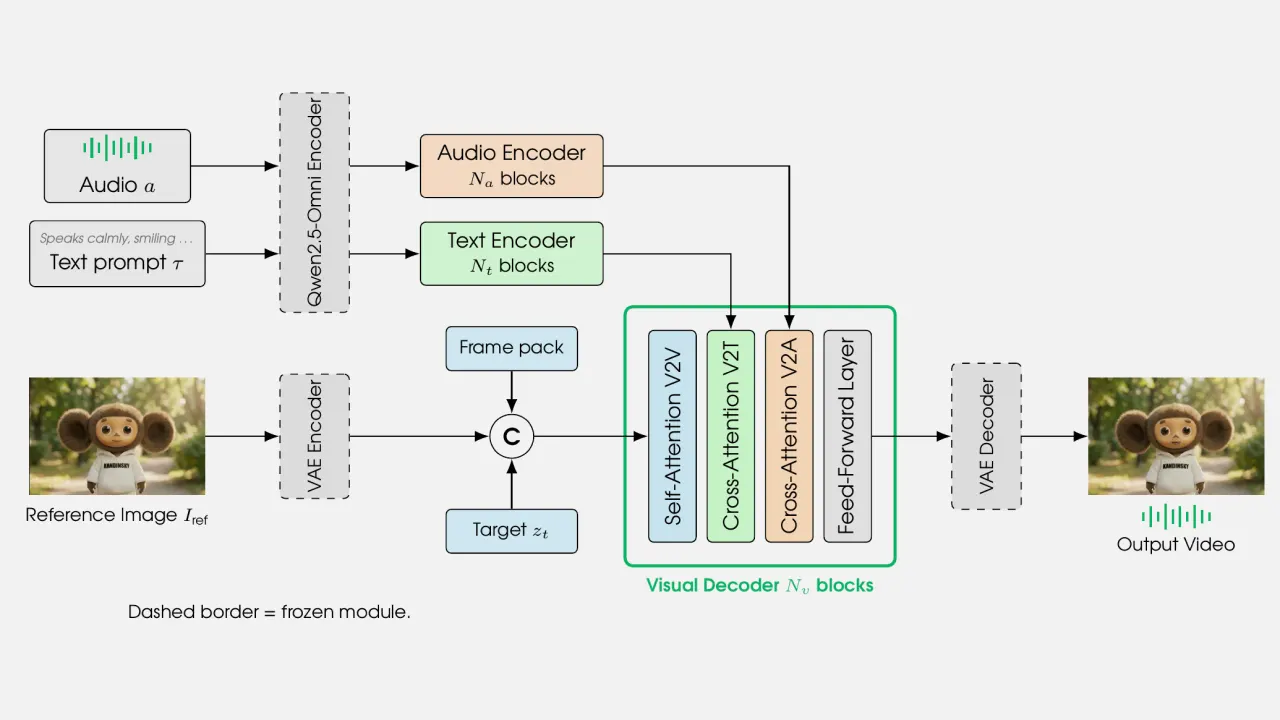
Sber Open-Sources Kandinsky Avatar 1.0 Talking Avatar Model