@cosme Data Breach Exposes Info of About 3 Million Members
Istyle, operator of the beauty site @cosme, says unauthorized access leaked data on roughly 3 million members, including names, addresses and birth dates.
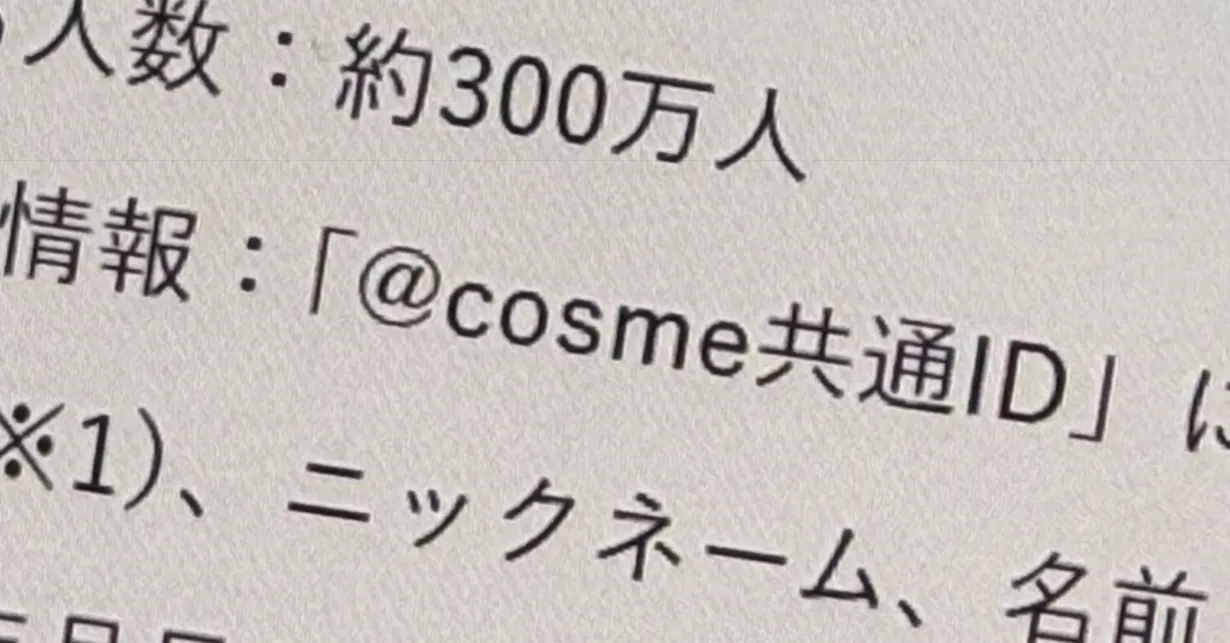
Istyle, the company behind the Japanese beauty site @cosme, announced on November 2 that a third party gained unauthorized access to its systems and that data on about 3 million members registered under the "@cosme Common ID" has leaked.
The exposed information includes names in kanji and kana, postal codes, addresses, phone numbers, email addresses, automatically assigned user IDs, gender, dates of birth, nicknames, skin type and hair type. According to the company, login passwords and credit card data have so far been confirmed as not included.
Former members also affected
Istyle confirmed the leak on October 28. It has not disclosed when the intrusion took place or how the attacker got in. Anyone who was a member at the time of the unauthorized access is covered, even if they have since cancelled their account.
The company is working with an outside security firm to determine the cause and the scope of the impact. Based on the findings, it plans to consider and implement measures to prevent a recurrence.
Notification schedule
Affected users will be contacted individually through the contact details Istyle holds, with notifications due to be completed on November 6. Emails will be sent from the "cosme.net" domain. For former members, the company will use information it retains for a set period after cancellation under its privacy policy.
Because the leaked data combines identity details with contact information, affected users may want to be alert to phishing emails, texts and calls that use their personal details. Checking that any message claims to come from the cosme.net domain is a sensible first step before clicking links.
This is not the first security incident for the service: Istyle previously warned that more than 10,000 users' email addresses may have been exposed because of a file-transfer service misconfiguration. The latest breach adds to a run of large Japanese consumer data leaks this year.
Apps worth a look
 SUMO: the number puzzle
Tap the right tiles, add them up, hit the target. Easy to learn, hard to master. Free, for all ages.
 Dialo: learn languages by speaking
Talk to an AI conversation partner; every sentence comes back corrected and explained in your language. 9 languages, A1 to C2.
 ediviewer: read EDI files like documents
Open EDIFACT and X12 messages, see every segment explained, convert to JSON/XML, export PDF and Excel. Runs locally, no upload.
More from this day
See all →
Germany's BSI warns politicians of possible iPhone spyware attack
BMW to offer partially automated city driving from 2027
Apple Reportedly Plans Three iPad Updates for Early 2027