Google Says Videostrong Turned 1.3 Million Android Boxes Into a Botnet
Google says Android partner Videostrong built a backdoor into 1.3 million devices and ran it as a botnet. The company has dismantled it and cut ties with the manufacturer.
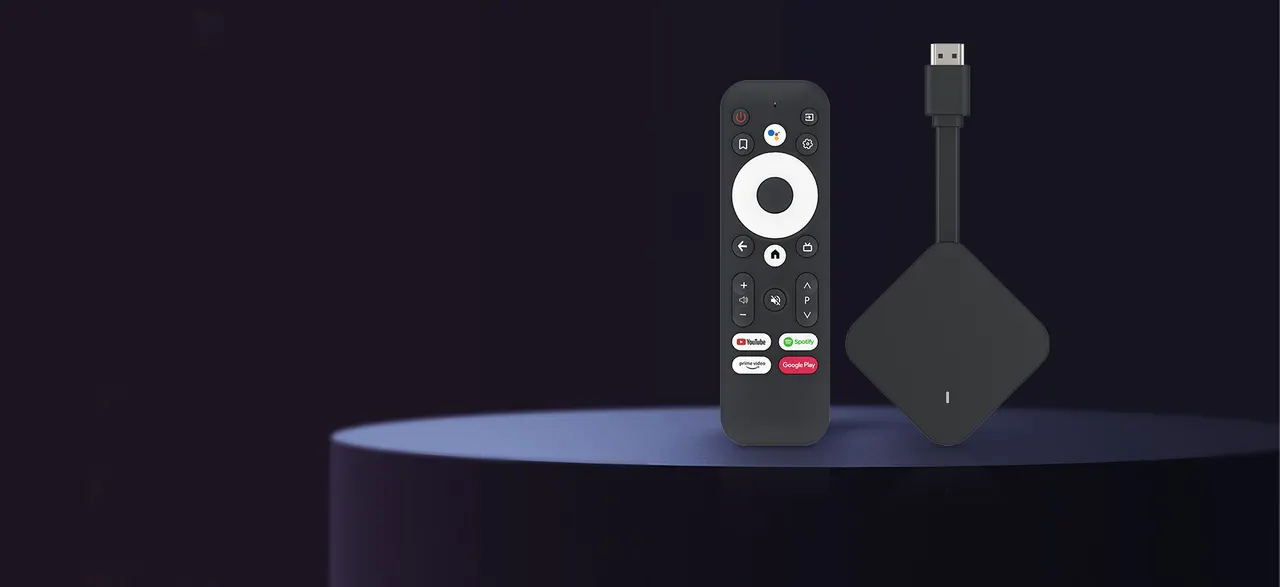
Google says one of its Android manufacturing partners secretly built a backdoor into 1.3 million devices and turned them into a botnet. The company says it has dismantled the backdoor and "cut ties" with the maker, Shenzhen-based Videostrong Technology Co., which is now banned from building or selling certified Android devices and from supplying software for them.
What the botnet did
According to Google, the infected devices were used without their owners' knowledge for "malicious activity" such as ad fraud, data exfiltration and routing unauthorized network traffic. The company argues the backdoor and botnet were "intentionally developed, deployed, and operated for financial gain."
Google says Videostrong monetized the backdoor by selling access to criminal affiliates and loading their malware modules onto infected hardware. Those modules carried out ad fraud, silently enrolled devices in residential proxy networks and installed further malware on devices compromised through the XCPE backdoor.
Many models, multiple years
The problem was not limited to one product. Google says the malware was built directly into many device models and brands over several years. Most were Android TV set-top boxes, but the botnet also reached other Android-based IoT devices, including telehealth devices, karaoke machines and digital signage.
Videostrong used obfuscation techniques to load the malware after users booted the hardware for the first time, according to Google.
Wider takedown
Google also moved against the command-and-control domains that operate the affiliate modules. Because those affiliates distribute their modules through channels beyond XCPE, the company assesses that the takedown will cut access to at least 10 million additional compromised devices.
Google says it has changed its review process for device manufacturers following the incident. For buyers, the case shows that low-cost certified hardware can ship with malicious code already installed, which is hard for owners to detect.
Apps worth a look
 SUMO: the number puzzle
Tap the right tiles, add them up, hit the target. Easy to learn, hard to master. Free, for all ages.
 Dialo: learn languages by speaking
Talk to an AI conversation partner; every sentence comes back corrected and explained in your language. 9 languages, A1 to C2.
 ediviewer: read EDI files like documents
Open EDIFACT and X12 messages, see every segment explained, convert to JSON/XML, export PDF and Excel. Runs locally, no upload.
More from this day
See all →
iPad Buying Guide: Why Waiting for Apple's 2027 Lineup Pays Off
Lenovo Smart Clock shows wrong time in Canada after DST end
Binance Hack: FBI Blames North Korea's TraderTraitor for $6B Theft
Gallium Defense Raises €7.1M for Low-Cost Drone Detection Radar
More in: Security
See all →
Microsoft: North Korean Jasper Sleet Uses AI to Fake Job Applicants

Hacked Alert Apps in Russia and Ukraine Send Fake Nuclear Warnings

LLMjacking: Hackers Run Up $100,000-a-Day AI Bills for Firms
